Blog
Read article
About this service
Build scalable, maintainable software with our experienced engineering teams. We deliver high-quality code and best practices that help your product succeed.
Go to serviceTechnical due diligence
Independent technical due diligence for investors, founders, and acquirers in the Belgian and Benelux market. We assess software and the engineering teams that build it, not buildings or technical installations. Based in Leuven, working in English, Dutch, and French. 190+ audits since 2008.
You call us when a big decision depends on understanding the true state of the technology. The trigger is different every time. The need is always the same: clarity.
One thing worth saying up front, because the phrase is crowded in Belgium. Property and energy consultancies also sell technical due diligence, and they mean a survey of a building, its installations, or a renewable energy asset. That is a different trade. We look at software: the codebase, the architecture, the people who ship it, and the way they work.
You are evaluating a SaaS company for investment. You need an independent technical assessment to understand the real state of the product, the team, and the risks before you commit capital. Our due diligence gives you the clarity to invest with confidence or walk away with evidence.
You are acquiring a software company. You need to understand integration costs, hidden dependencies, and whether the existing team can execute your roadmap. We quantify the technical debt and assess handover readiness so there are no surprises on day 100.
You are preparing for a funding round. A self-initiated technical review signals maturity to investors and lets you fix issues on your own terms. We help you present your technology with confidence, backed by an independent assessment from engineers who have seen 190+ companies.
Every audit covers five pillars. Evaluating code alone is not enough. The strongest codebase in the world fails if the team, processes, or product direction are broken.
Composition, roles, psychological safety, feedback culture, hiring practices, and key person risk. We assess whether the team can execute the roadmap independently.
CI/CD maturity, deployment frequency, code review practices, release workflows, incident response, and retrospective culture. The operational backbone of engineering.
Onboarding guides, architecture decision records, knowledge distribution, and language barriers. 23% of Belgian companies we audit flag non-English documentation as a scaling ceiling.
How the product is built, what it runs on, test coverage, where technical debt lives, and what the scalability ceiling looks like. Includes secrets management, access controls, data handling, and GDPR posture, which matter for EU companies working across borders.
Roadmap clarity, metrics tracking, prioritisation discipline, discovery practices, and alignment between the technical solution and the business problem.
After 190+ technical audits across seed rounds, Series A, and M&A due diligence, the patterns are remarkably consistent. Companies think their situation is unique. The problems repeat.
have documentation debt
lack automated testing
have key person dependency
have a weak or missing roadmap
have rudimentary product management
have secrets committed to their codebase
These numbers come from our benchmark study across 190+ SaaS companies. The average company shows 15 to 20 concerns. Top quartile companies have fewer than 10. Knowing where you stand relative to the market is the first step toward fixing what matters. The technical due diligence checklist shows the five areas we assess and the red flags we look for.
Belgian and Benelux investors have started asking about AI adoption in the same breath as architecture and team. We answer it the way we answer everything else, by looking at the repository and talking to the people who write the code, and it lands in the same report rather than in a separate exercise.
It cuts both ways. A codebase largely written with AI gets the same scrutiny as any other, plus the questions specific to how it was made.
Five steps. 10 business days. From the first conversation to a report your board can act on.
A 30-minute conversation to understand your situation, timeline, and what you need from the audit. We define the scope and agree on logistics.
A 2-hour session with the CTO or technical lead. We map the landscape, identify focus areas, and schedule interviews with key team members.
Our team reviews the codebase, systems, and documentation. We conduct stakeholder interviews to understand how the team thinks about their work.
We document observations and concerns across all five pillars. A draft goes to the company for factual review before the final version.
We walk through the report, answer questions, and discuss priorities. We join board meetings if needed. From baseline to debrief: 10 business days.
The deliverable is a comprehensive report designed for two audiences: board-level stakeholders who need the summary, and technical leaders who need the detail.
A concise overview of findings and key recommendations. Written for investors and board members who need to make decisions without reading 25 pages of technical detail.
Detailed observations and concerns across all five pillars. Each finding includes context, severity, and specific recommendations. Typically 20 to 25 pages.
A prioritised list of improvements, ordered by impact and urgency. Designed to be immediately actionable by the engineering team, with clear milestones.
A live walkthrough of the report with all stakeholders. We answer questions, clarify priorities, and join board meetings if needed. No findings left unexplained.
Belgian investors and acquirers are familiar with financial due diligence. Technical due diligence answers a different set of questions entirely.
| Technical DD | Financial audit | Internal review | |
|---|---|---|---|
| Focus | Code, architecture, team, processes | Accounting, valuation, compliance | Self-assessment by internal team |
| Conducted by | Senior engineers and CTOs | Financial auditors (Big 4) | Internal engineering team |
| Independence | Fully independent, NDA-protected | Fully independent | Limited (self-reporting bias) |
| Covers team dynamics | Yes (interviews, culture assessment) | No | Partially |
| Covers scalability | Yes (architecture, infrastructure) | No | Partially |
| Timeline | 10 business days | 4 to 8 weeks | Varies (often deprioritised) |
| Best for | Investment decisions, M&A, scaling | Regulatory compliance, valuation | Continuous improvement |
We have been building and evaluating software from Belgium since 2008. That gives us something no international consultancy or automated tool can match: local context combined with deep technical expertise.
No Belgian competitor comes close to this track record. We have seen the patterns, the surprises, and the red flags across every stage and industry. Our benchmark data means we can tell you exactly where you stand relative to the market.
Face-to-face interviews in Brussels, Ghent, Antwerp, or Amsterdam. We work in English, Dutch, and French. For Belgian companies scaling internationally, we flag language barriers that become real problems at 10 to 15 engineers.
PMV, Capricorn Partners, Holland Capital, Smartfin, Knight Capital, and The Faktory Fund have all commissioned audits from us. Investor referrals convert at 75% because the people who have seen our work keep coming back.
Teams that feel helped rather than judged tell the truth. That matters. An adversarial audit gets defensive answers. Ours gets honest ones. The result is a report that reflects reality, not a sanitised version of it.
If the report reveals issues that need fixing, we can help. CTO coaching, fractional CTO services, and software engineering support are all available as follow-up. Many clients start with an audit and evolve into a longer relationship. No obligation, but the option is there.
You will not see companies like Amazon among our past clients. You will, however, see the names that will soon rock the SaaS world because we helped them predict risks and avoid failure.
“Madewithlove was the only party advising us to refactor instead of starting over. With hindsight, this was the right choice. Our customers started feeling the difference right away and didn’t have to wait 9 months or longer for improvements.”
Steven Debrauwere
CEO, Contractify
“A strong partner for tech due diligence: clear, rigorous, and always pragmatic, with reports that are easy to navigate and act on.”

Gaëtan Baudelet
Partner, Rise PropTech
“If you can tell VCs, ‘we are working with madewithlove’ they already know it will be quality because they have also used madewithlove to do, for example, audits.”
Thomas Vanhumbeeck
Cofounder & CEO, FixForm

FROM 190+ SAAS AUDITS
51% mishandle credentials in the codebase
The finding investors react to hardest.
The security hole nobody talks aboutWe have conducted technical due diligence for investors and companies across Belgium and Europe, from seed stage to M&A.
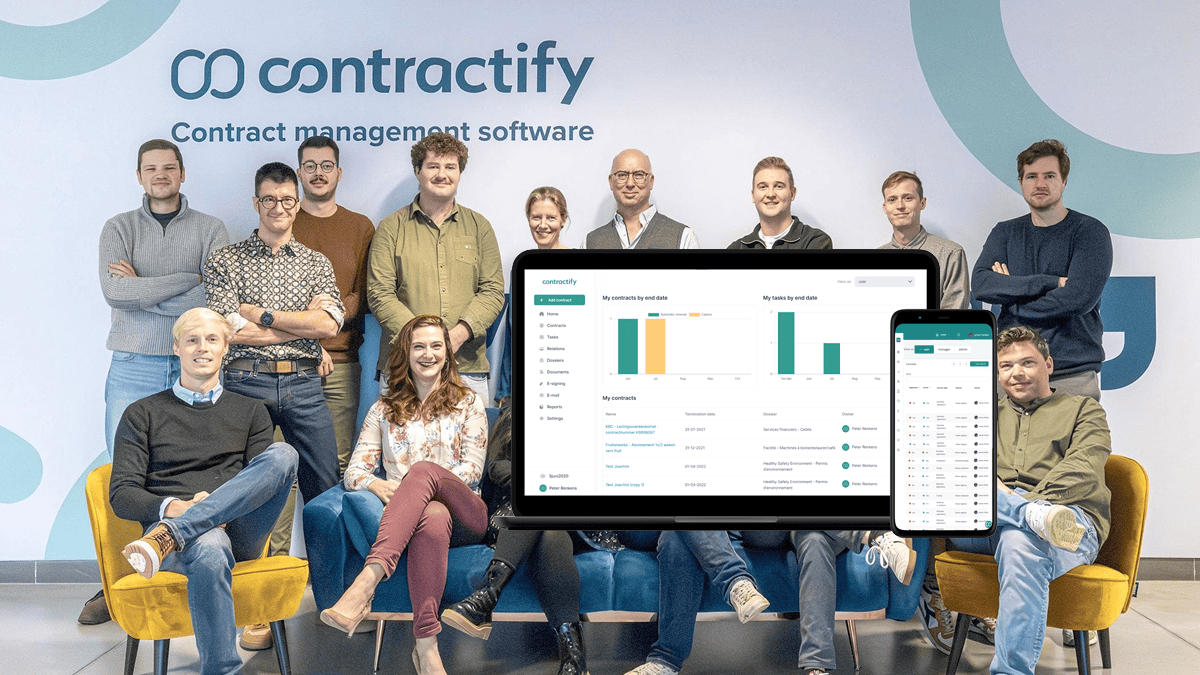
Contract management simplified through refactoring, not rewriting
We were the only party advising them to refactor instead of starting over. Over 18 months, we modernised their PHP/Laravel stack, established CI/CD pipelines, migrated infrastructure to DigitalOcean, and dramatically reduced bug rates while mentoring their growing team.

Our latest thinking on technical due diligence, audits, and what makes SaaS codebases investable.
Newsletter
Investor Insights is our monthly email for people who invest in software companies: three findings from recent technical due diligences, three questions for your next board meeting, and a word from Andreas Creten. Free, short, and written to be read between two meetings.
Tell us about your company or portfolio company and we will define the right scope for your technical due diligence. No commitment, just a conversation.
Everything you need to know about technical due diligence in Belgium.
Technical due diligence is an independent evaluation of a company's technology, codebase, team structure, and engineering processes. It replaces assumptions with objective facts, giving investors and founders a clear view of technical strengths, weaknesses, and risks before major decisions like investments, acquisitions, or scaling. Some people call it a technical audit, but the scope goes well beyond a simple code review.
No, and the phrase is genuinely ambiguous in Belgium. Property, construction, and energy firms use technical due diligence to mean a survey of a building, its installations, or a renewable energy asset ahead of a real estate transaction. We do not do that work. Our technical due diligence covers software: the codebase, the architecture, the engineering team, and the processes behind a SaaS product. If you are buying a building, you want a surveyor. If you are investing in a software company, you want us.
Financial audits (Deloitte, PwC, KPMG) evaluate accounting, valuation, and compliance. Technical due diligence evaluates the engineering side: code quality, architecture decisions, team capability, security posture, and scalability. Both are needed for thorough due diligence, but they answer fundamentally different questions. Financial audits tell you what the numbers say. Technical DD tells you whether the product can deliver on its promises.
Our standard process runs 10 business days from the baseline interview to the final report. This includes stakeholder interviews, code review, systems analysis, and a comprehensive debrief. For urgent deal timelines, we can compress to 5 business days with a focused scope.
The cost depends on scope and complexity. A standard audit for a seed-stage company with a small team costs less than a full-scale due diligence for a Series B acquisition target. Contact us for a scoping call where we can give you a precise quote based on your situation. Our pricing reflects the seniority of the team: every engagement is led by experienced CTOs and staff engineers.
Yes. We are based in Leuven and work across the entire Benelux region. We conduct due diligence for companies in Brussels, Ghent, Antwerp, Amsterdam, Rotterdam, and beyond. Our team works in English, Dutch, and French, which removes language barriers during interviews.
Every engagement is led by senior staff engineers and experienced CTOs who have spent years building and scaling SaaS products themselves. No juniors, no outsourced evaluations. The people who write the report are the same people who interview your team and review your code.
We evaluate five pillars: team and leadership (psychological safety, feedback culture, hiring practices), processes (workflows, code reviews, retrospectives), written communication (documentation, knowledge management, onboarding), engineering practices (CI/CD, testing, technical debt), and problem-solution fit (vision, roadmap, customer validation).
You receive an executive summary for board-level stakeholders, a detailed technical report with observations and concerns per pillar, and an action roadmap prioritised by impact. We follow up with a debrief session and can join board meetings to present findings.
Yes. A growing share of the codebases we assess were written largely with AI tools. We verify quality, security and maintainability with the same five-pillar methodology, and we add the questions specific to AI-built software: whether the generated code is covered by tests, whether anyone reviews what the tools produce, and whether the team can still explain how the system works.
Yes, as a standard part of every audit. We look at how the team uses AI today and check it against what is in the repository, because what shows up in commits, pull requests and documentation is regularly more than what came up in the interviews. We also look at whether guardrails and review discipline exist, where source code is allowed to go and whether those controls are proportionate to the other risks we find, how dependent the product is on a single model provider, whether spending on AI matches the adoption we can observe, and whether the codebase is documented well enough for AI tools to work on it safely.
More often a mismatch than an absence. A pattern we keep seeing: serious money going into AI infrastructure and experimentation while practical adoption in the product stays thin, alongside strict rules to keep source code away from public models while broad production access, shared credentials and secrets sitting unencrypted on machines get far less attention. That goes in the report as one finding about alignment, with the evidence behind it, because what has to change is the order of priorities rather than the tooling.
No. About half our engagements are commissioned by investors doing pre-investment due diligence. The other half come from founders who want clarity before a funding round, boards requesting an independent technical assessment, or companies preparing for an acquisition (on either side of the deal).
The report gives you a clear picture and a prioritised action plan. If you need help executing on the findings, we offer CTO coaching, fractional CTO services, and software engineering support. Many clients start with a due diligence and evolve into a longer advisory relationship. But there is no obligation to continue.